
The strongest version
Quantum computers running Shor's algorithm could derive private keys from public keys, letting an attacker spend anyone's coins. When that happens, Bitcoin is finished.
What is actually at risk
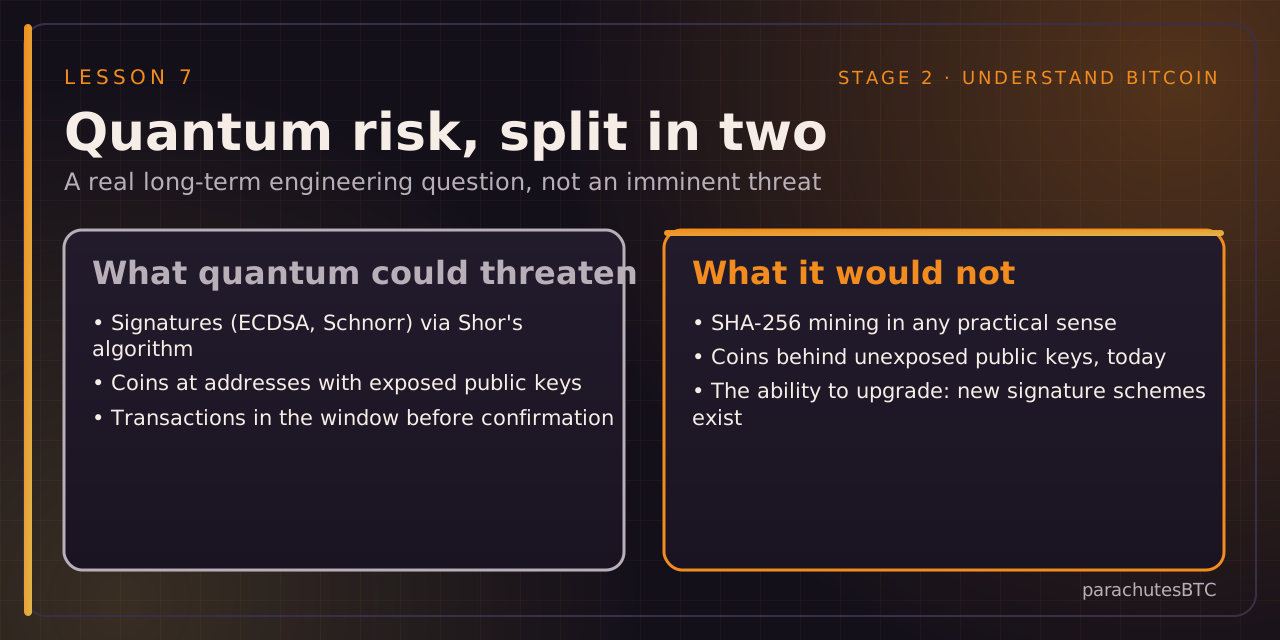
- Signatures. Bitcoin's ECDSA and Schnorr signatures rely on math a sufficiently large quantum computer could break. The same math secures every bank, government and website on Earth.
- Exposed public keys. A key is revealed when an address is spent from. Coins at reused addresses and in very old pay-to-public-key outputs (including Satoshi's) would be exposed first. Estimates put several million BTC in that category.
- The confirmation window. A transaction reveals its public key when broadcast; a fast enough attacker could race it.
What is not
- Mining. Grover's algorithm offers only a modest speed-up on SHA-256; quantum mining is not a practical threat.
- Unexposed keys, today. Addresses that have never been spent from show only a hash.
The engineering answer
Estimates of the qubits required range from millions to hundreds of millions of error-corrected qubits; today's machines are at a few thousand noisy ones. Post-quantum signature schemes exist and are standardised; proposals such as BIP 360 describe how Bitcoin could add a quantum-resistant address type by soft fork. Migration would take time and block space, which is why the work is being discussed now rather than later.
What remains true
This is a real, long-term engineering question for Bitcoin and for all of cryptography. It is not an imminent threat, and Bitcoin is in a better position to coordinate an upgrade than most systems because the problem is public and the community is paying attention.